

WASHINGTON—At the end of October, North Korea-based TraderTraitor hit the trading platform Binance with the largest cryptocurrency theft in history, moving more than six billion dollars out of hot wallets. The massive size of the theft is what strikes many people first, and I count myself among them. But I was also struck by a sense of déjà vu.
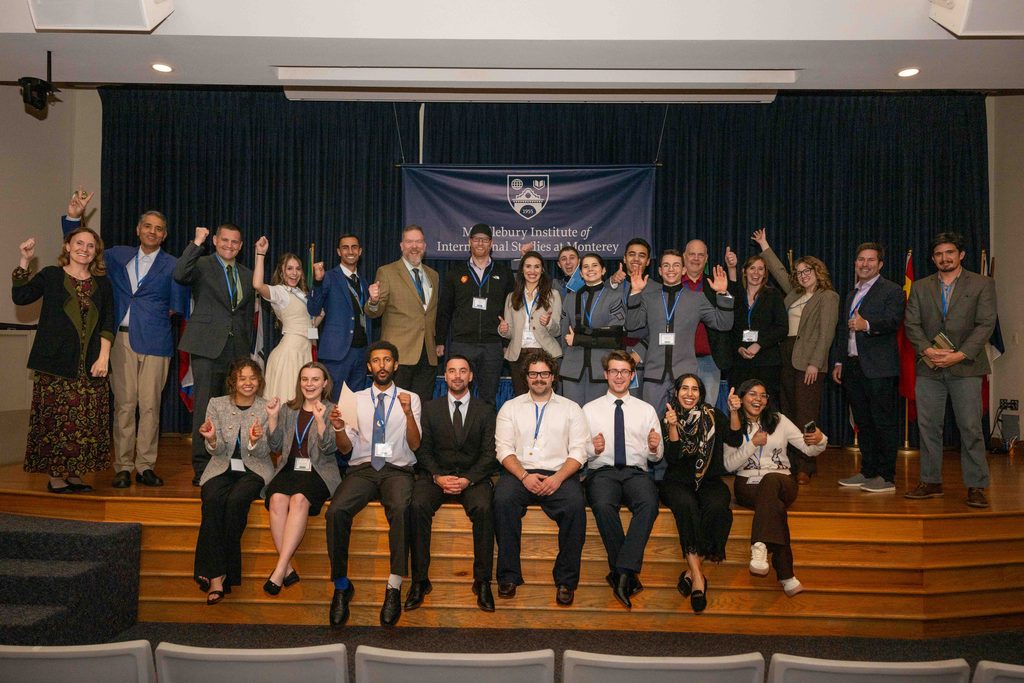
Last November, I helped organize the Atlantic Council’s Monterey Cyber 9/12 Strategy Challenge, a competition in which college students develop policy responses to simulated cyber crises. At that event, several teams were presented with a fictional scenario that shared some of the characteristics of the Binance hack, and they were tasked to develop strategies to mitigate the imagined cryptocurrency theft before it got worse. Their recommendations anticipated several important responses to the real attack, but the Binance hack also exposed gaps in their approach, particularly the human vulnerabilities that allowed attackers to breach the exchange in the first place.
The scenario
At Cyber 9/12, a competition program run by the Atlantic Council for the past fifteen years, students from around the world work in teams of three to four to develop policy recommendations for a relevant government body, represented by expert judges, in response to an escalating cyber crisis. These crises are always based partly on past or potential real-world cyberattacks. For our Monterey competitors, we designed the scenario around a cryptocurrency heist.
In the exercise, AuriXchange, a fictional US exchange modeled after companies like Binance and Bybit, lost two billion dollars from cold wallets through a targeted spear-phishing campaign. The North Korean-linked hackers in our scenario successfully stole employee credentials and moved laterally through AuriXchange’s system, eventually gaining access to cold wallets and the funds they held. The scenario hinted at the funds being moved through peel chains and mixers, strategies consistent with past North Korean money-laundering schemes, though attribution was purposefully obfuscated for students to determine with or without confidence.
The process of attribution was further complicated when a prominent technologist offered a bounty for information on the stolen funds, drawing vigilante hackers into the fray and making the field of play noisier. We also included reports on the expansion of North Korea’s General Satellite Control Center, meant to suggest to students where the stolen funds might be funneled.
Several Monterey teams developed useful policy responses to the fictional incident. Four recommendations from the top-performing teams offer lessons for responding to cryptocurrency hacks like October’s Binance attack.
Lesson 1: Freeze stolen funds quickly, but don’t confuse freezing with recovery
Several teams called for rapid freezes of the stolen funds and treated those freezes as a public-private, cross-border task. For example, one team recommended that the US Treasury’s Financial Crimes Enforcement Network (FinCEN) work with exchanges and partners to flag and quarantine tainted wallets and request allied freezes via the US State Department. Another team suggested a freeze-and-recover strategy through the Five Eyes intelligence alliance, Interpol, Europol, the Egmont Group, and Chainalysis.
In the real-life Binance hack, freezes began within an hour of the first unauthorized transfers, and about $2.8 billion had been frozen or intercepted as of writing. The speed and scale of the response are dramatically stronger than those of the Bybit hack in February of 2025, which inspired our scenario. Two months after that theft, only 3.84 percent of the stolen funds had been frozen, and more than a quarter had gone dark.
What made the Binance incident different is that stablecoin issuers Tether and Circle moved quickly to freeze stolen tokens. The speed with which they were able to do so still depended largely on voluntary cooperation. So, formalizing the network of exchanges, blockchain analytics firms, financial intelligence units, and stablecoin issuers our students suggested would make rapid freezes a standard procedure rather than one dependent on goodwill. Freezing stolen assets, however, is only the first step: Recovering and returning them is a separate challenge.
Lesson 2: Be ready to attribute when the facts come in
Our Cyber 9/12 competitors recommended relevant analysis and mitigation techniques, but they were far more cautious about publicly attributing the hack to North Korea than analytics teams and the US government were in reality. One suggestion was to have the Federal Bureau of Investigation (FBI)’s Virtual Asset Exploitation Unit and the Secret Service’s Global Investigative Operations Center lead a blockchain forensics surge, drawing on FinCEN intelligence, before attributing with confidence. Another team recommended forming a Central Intelligence Agency (CIA), National Security Agency, and FBI collaboration with an 80 percent attribution confidence threshold. This team also rejected early public attribution to avoid misattribution and the risk of escalation.
For October’s incident, TRM Labs and Chainalysis attributed the hack to TraderTraitor within hours, supported by evidence that funds from last month’s Bitget hack (already attributed to TraderTraitor) were commingled with the recently stolen Binance funds. The FBI confirmed the attribution two days after the hack, though North Korean officials have denied involvement.
In fairness to our students, the scenario we gave them rewarded their caution. Later in the competition, we fed them deliberately misleading intelligence, with vigilante hackers pointing at a China-based group and an NSA report blaming that group for a separate cyberattack on a hospital.
Real cases may be less murky, as was the case with Binance. When stolen funds commingle on-chain with those from earlier, already attributed thefts, and the methods used match a known group, attribution becomes both fast and reliable. At that point, delaying action despite strong evidence can cost valuable time for mitigation measures such as freezes and sanctions.
Lesson 3: Sanction the cash-out networks, not just the hackers
Which brings us to our third takeaway. Monterey students favored sanctions as a response, but not necessarily against North Korea. For instance, one team recommended that the Office of Foreign Assets Control target identified wallets and related entities with sanctions, with the US State Department pressing allies to mirror them. The team also suggested that the US Marshals Service and the Justice Department’s Money Laundering and Asset Recovery Section manage forfeited assets. Another team proposed a US-only approach, expanding sanctions lists to intermediaries and preparing sealed indictments for follow-on action.
The hackers have yet to convert the stolen crypto into fiat currency. Since money-laundering schemes ultimately depend on converting or using illicit proceeds, another round of sanctions on North Korea would add little to the pressure Pyongyang already faces. Targeting the wallets and intermediaries that convert crypto to cash could have the most impact by pressuring the scheme where it’s weakest.
One of the competing student teams also offered a timely asset-recovery recommendation. Binance says it has already replenished 98 percent of the affected assets from its own reserves. That leaves an open question about the nearly $3 billion that has been frozen, specifically, who is entitled to it, and through what process can those assets be recovered?
Lesson 4: Build legal scaffolding before the next attack
Stolen cryptocurrency can move across borders in minutes, while international legal cooperation can take months. One of the team’s most creative recommendations therefore looked ahead, past the immediate crisis, to consider where stolen funds were likely to end up.
The team proposed that the Justice Department’s Office of International Affairs and its Computer Crime and Intellectual Property Section open talks with the Association of Southeast Asian Nations (ASEAN). The goal would be to create expedited channels for mutual legal assistance requests on asset tracing, plus memoranda of understanding for cases involving digital asset theft.
The idea isn’t without precedent. In October 2025, an eleven-country multilateral sanctions monitoring team found that North Korea had used Cambodia’s Huione Pay to launder proceeds from major thefts. The US Treasury had already moved to cut Huione off from the US financial system, but mutual legal assistance requests typically take months. The expedited channels students proposed would allow authorities to coordinate across borders before stolen disappear.
Where scenario and reality diverged
While several lessons from our November 2025 exercise are relevant here, the differences between our scenario and the October Binance hack also reveal two urgent gaps in the students’ responses.
First, in reality, the exchange absorbed the financial loss. In our scenario, AuriXchange’s losses triggered market panic. Several teams proposed relief for victims or backstops for banks. For example, one suggested a Treasury-led relief program, and another recommended Exchange Stabilization Fund support. Binance instead covered the losses from its own insurance funds and reserves, and Bitcoin’s price only dropped about 5 percent overall. Domestic regulatory fixes also have limited reach over a global exchange like Binance. The contrast highlights an unresolved question over who should bear the costs of major thefts and what happens when an exchange can’t cover losses on its own.
Second, the attackers targeted people, and our students’ fixes focused on wallets. Our scenario also began with social engineering, but the teams’ remedies centered on wallet custody: multisignature keys, air-gapped servers, and cold-storage standards. According to Binance’s own account, North Korean operatives posing as recruiters approached a Binance engineer on LinkedIn, ran him through two rounds of fake interviews, and persuaded him to download a malicious “technical assignment” that compromised his computer. The attacks then used an internal AI tool to take control of additional employee credentials until they gained the permissions they needed to access the exchange’s wallets. None of the teams treated the targeting of exchange staff as a policy problem in its own right.
Preparing for the next crypto heist
A year before the largest crypto heist in history, university students responded to an eerily similar scenario and identified many of the measures needed to effectively respond to such a heist. The real incident highlighted the importance of preparing for human vulnerabilities and resolving questions of liability and asset recovery.
These lessons showcase the value of exercises like the Atlantic Council’s Cyber 9/12 Strategy Challenge not only in preparing future policymakers to respond to crises, but also in identifying gaps before the next one strikes.